1Password CLI: secrets out of your env file | made with ngram

About the video
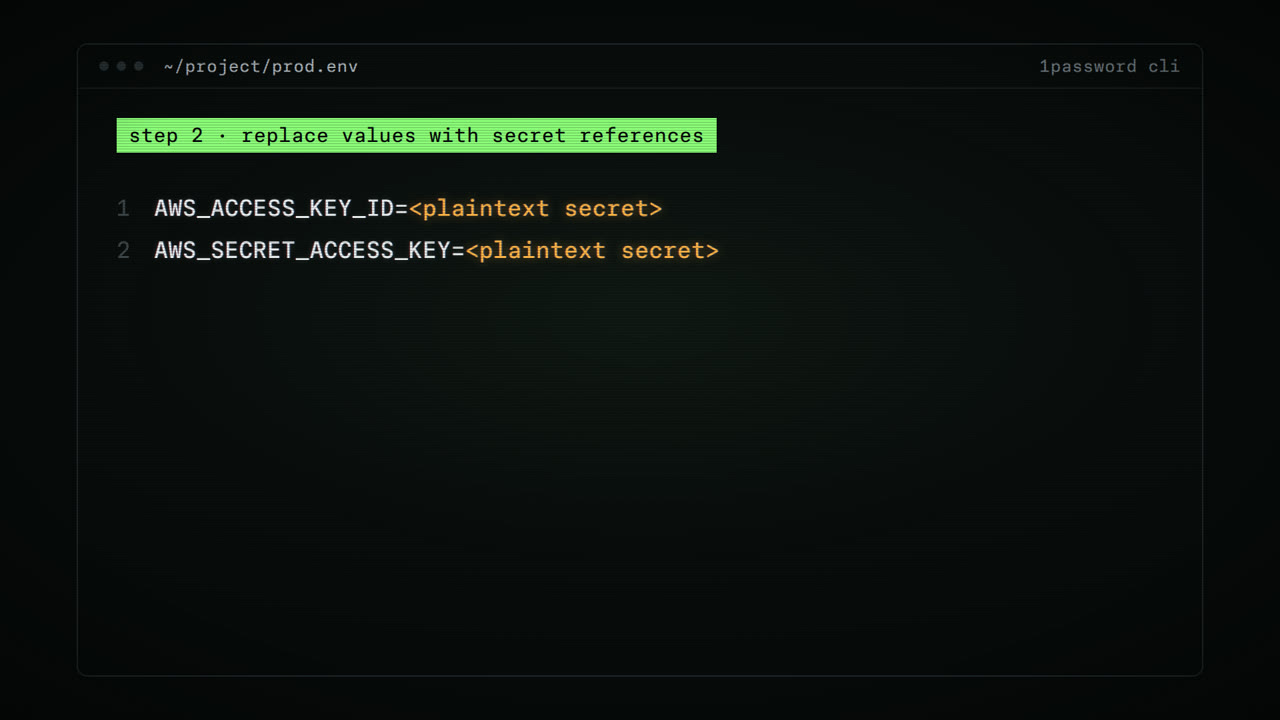
This video was created by ngram to explain how the 1Password CLI keeps secrets out of project files. It walks through the risk of hardcoding secrets in plaintext, where they can be exposed, and shows the fix: storing each secret in a 1Password vault and replacing its value in an environment file with a secret reference, a URI pointing to where that secret lives. The video makes clear that the checked-in file holds only references, never the secrets themselves. It then covers op run, which loads the secrets at runtime and executes the command in a subprocess, making the secrets available only for the duration of that process. The video closes with an end card inviting viewers to explore 1Password CLI further. Using HTML/CSS motion graphics, ngram built out five scenes, titled The risk, Store and reference, The file you check in, op run, and End card, to walk through this workflow step by step on a 16:9 canvas, pairing each concept with matching on-screen visuals synced to the narrated script.
- #1Password CLI
- #secrets management
- #environment variables
- #developer tools
- #security
- #command line